Drianta security: regulation, technology and asset protection
A crypto investment platform handles other people's capital — and that responsibility brings clear obligations with it. We don't bury those obligations behind vague language. Drianta operates under active regulatory oversight, applies institutional-grade data protection and builds its infrastructure so that user risk stays minimal.
Regulation and supervision
Drianta holds a licence from the Gibraltar Financial Services Commission (GFSC) as a Distributed Ledger Technology Provider, No. 893378. What this means in practice:
We operate under active oversight — not in a regulatory grey zone.
The GFSC is a government body that examines how a firm safeguards client assets, meets AML/CFT standards and maintains corporate governance. Under Gibraltar's DLT framework, storing or transmitting client value via distributed ledger technology requires authorisation and ongoing supervision.
The regulator carries out regular supervision.
The GFSC applies a risk-based model: scrutiny scales with the size and risk profile of operations. This isn't a one-off licence — it's ongoing oversight, including thematic reviews and on-site inspections of how DLT Providers handle client assets.
Client asset protection is built into the framework.
Principle 5 of the DLT Regulations requires client crypto assets to be held separately from the firm's own funds — clearly designated, identifiable and protected from third-party claims. The GFSC also expects firms to reconcile client holdings daily.
We operate within the law.
Storing or transmitting client value via DLT in or from Gibraltar is a regulated activity requiring authorisation. Drianta holds that authorisation, along with a contingency plan for an orderly wind-down if necessary.
Technology and security
Data and infrastructure protection
Our security stack follows the same bar set for institutional finance: data is encrypted both in transit and at rest, access is tightly governed and the infrastructure passes regular internal and independent external audits.
Continuous monitoring
Client funds sit apart from the company's own capital — never commingled. That separation isn't decorative: it's what keeps client assets intact even if the platform itself hits trouble.
Segregation of assets
User funds are not mixed with the company's operating funds. This is a basic principle that protects client assets even if the platform runs into trouble.
Access control
Systems and data are closed by default. We work on least-privilege: each employee reaches only what their role demands, nothing more.
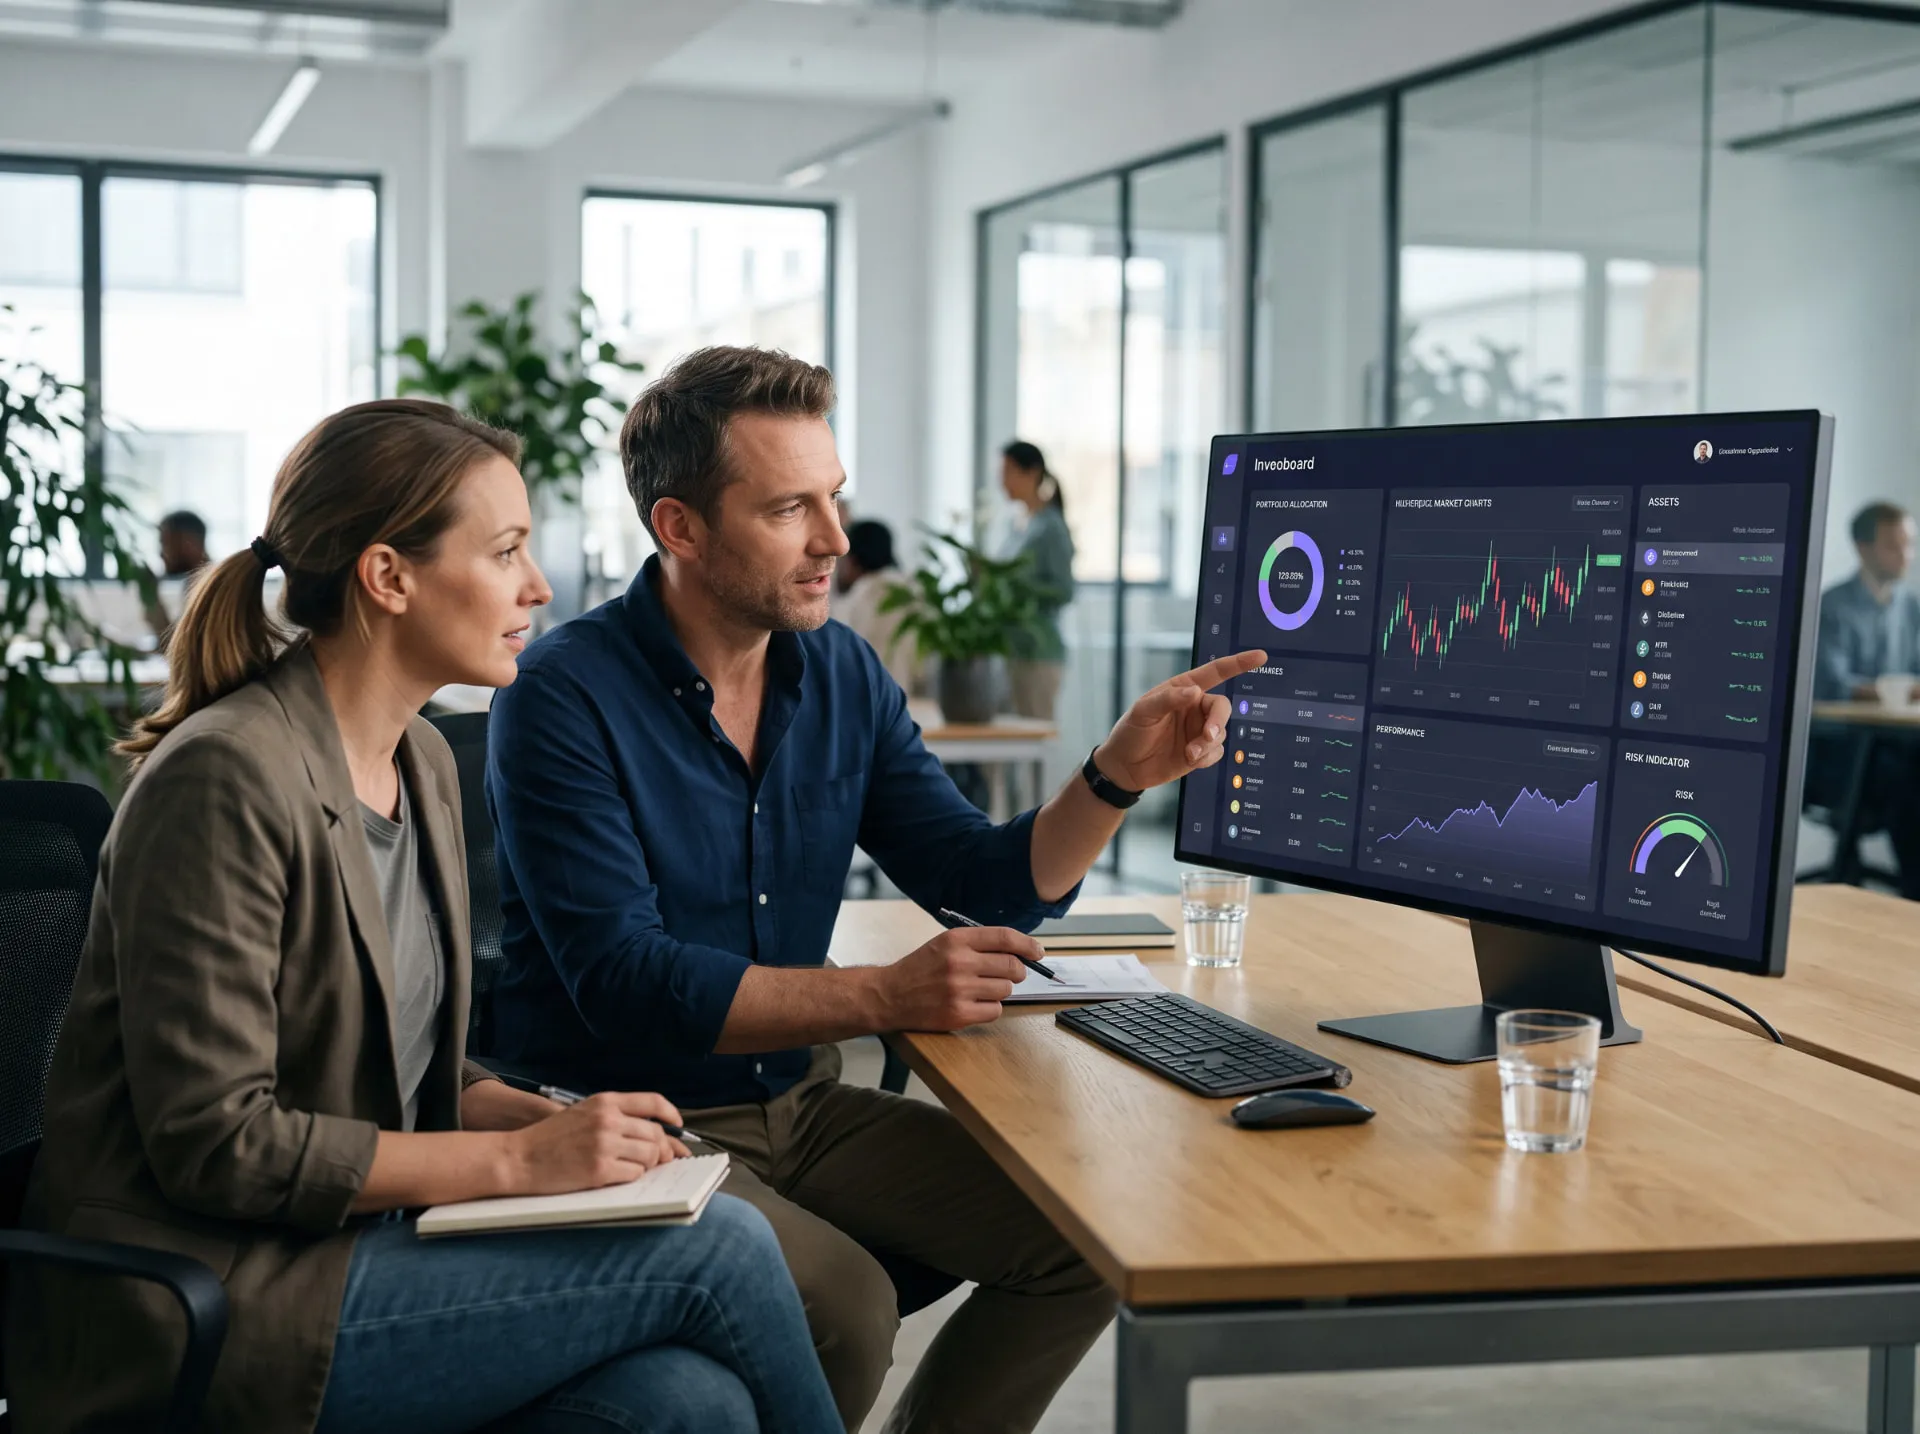
Still have questions about security?
Leave a request — and our consultant will answer your questions about regulation, data protection and how Drianta works with user assets.